SBOM Generation Locally Without Uploading Manifests Cloud
SBOM Generation Locally Without Uploading Manifests Cloud — a focused guide for ctos: what to do, what to measure, and what to avoid so this work stays separate from adjacent efforts.
Threat model for this choice
SBOM Generation Locally Without Uploading Manifests Cloud matters because code is IP. Cloud scanners upload snippets, manifests, and history; local-first keeps analysis in a SQLite file on the machine with zero telemetry. For regulated teams, that boundary is the procurement decision.
Data-flow you can show a CISO
Inputs stay local: repo read → local parse → SQLite write → local report/JSON export. Network calls in RefactorIQ: signed update check, optional user-token GitHub import, and explicit encrypted purchase claims — nothing else. No background upload, no account, 14-day offline grace.
| Control | Local-first | Typical SaaS |
|---|---|---|
| Code leaves machine | No | Yes (scan) |
| Telemetry | Zero | Usage + snippets |
| Air-gap viable | Yes | No |
See the privacy model end to end.
See privacy detailsProcurement pack for this case
Bring: architecture diagram, SQLite path and encryption-at-rest steps, telemetry disablement proof, JSON export sample, backup policy (encrypted copy to team drive). Redact snippets before any cloud upload; generate SBOMs locally without posting manifests. Reference: why local review matters with AI.
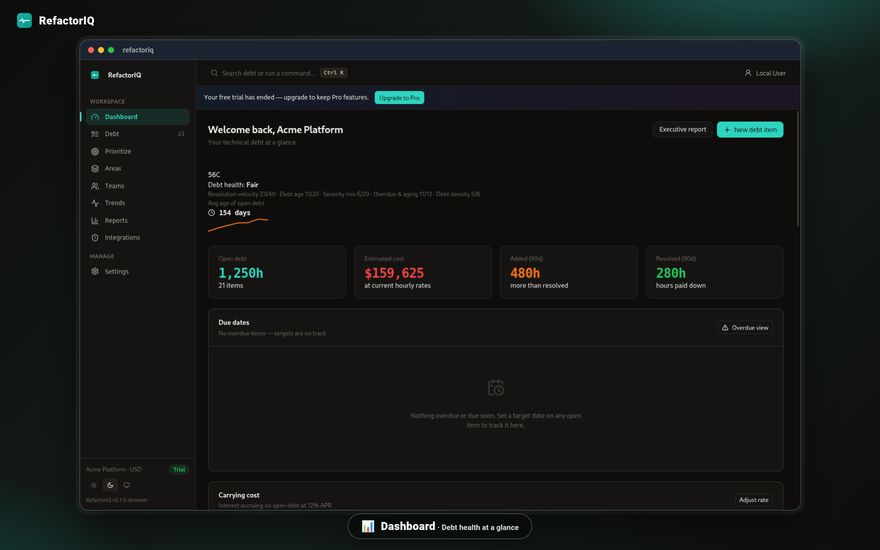
Operating offline
- Backup: versioned encrypted SQLite copies; restore is file copy.
- Audit: local append-only log of who priced and fixed what.
Try air-gap-ready tracking — free Demo.
Download RefactorIQReview this together with procurement pitch for local-first tools in one procurement pass so the data-flow boundary stays consistent.
What security review does not do
Security review protects IP and compliance; it does not price refactoring dollars, run sprints, or survey morale. Lock the data boundary here — hand value and velocity to their own owners.
Worked example: pricing this in dollars per day
The choice is not technical, it is economic. Take one item from this guide and price it the way the calculator on the product page does it:
principal = hours × blended rate
daily carrying cost = principal × APR ÷ 365
| Input | Value | What it tells you |
|---|---|---|
| Effort to fix | 19 h | Your estimate of the work, not the wish |
| Blended rate | $100/h | Loaded cost, not salary |
| Principal | $1,900 | The value sitting in the code |
| APR | 20% | Drag: slower changes, bugs, onboarding tax |
| Daily carry | ~$1.04/day | What waiting costs today |
| Yearly carry | ~$380/yr | What waiting costs for twelve months |
Run the same row twice before you believe it. Halve the hours and the carry still lands near $190 a year; double them and it is ~$760. That spread is a risk signal: if the range spans an order of magnitude, the estimate needs work before it can carry a decision.
One quarter of drift on this item costs about $95. That figure is the whole argument — it is small enough to be ignored in a roadmap review and large enough to matter once it compounds across a backlog.
What this guide does not cover
This post stays narrow on purpose. It does not go into refactoring ROI math, sprint prioritization, or burnout surveys, because those are separate decisions with their own inputs and their own audience. If you are weighing sBOM Generation Locally Without Uploading Manifests Cloud specifically, read this alongside Change Failure Rate Cost Model For VPs Engineering rather than trying to stretch either one to cover the other.
Key takeaways
- Price it before you argue about it. 19 hours at $100/h is $1,900 of principal; the debate about whether it matters stops being subjective once the number exists.
- Carry compounds quietly. ~$1.04 a day and ~$380 a year for this item, and it costs nothing to keep paying it.
- Name an owner and a date. Debt without a trigger is a wish; debt with a trigger becomes a line item.
- Show the range. Halve the estimate and the number still holds. If it does not, the estimate needs work, not the argument.
- Next step. Treat the range as a risk input when you sequence platform work.
FAQ
Is SBOM generation locally without uploading manifests safe for enterprise IP?
Start with sBOM Generation Locally Without Uploading Manifests Cloud: about 19 hours of work at a blended $100/h, or $1,900 of principal carrying roughly $1.04 a day. State that number, then the single business outcome it protects, then ask for dated capacity. If the ask is declined, log it with a revisit trigger so the decision stays visible to the cto.
How does SBOM generation locally without uploading manifests handle compliance?
Start with sBOM Generation Locally Without Uploading Manifests Cloud: about 19 hours of work at a blended $100/h, or $1,900 of principal carrying roughly $1.04 a day. State that number, then the single business outcome it protects, then ask for dated capacity. If the ask is declined, log it with a revisit trigger so the decision stays visible to the cto.
Why choose local-first for SBOM generation locally without uploading manifests?
Start with sBOM Generation Locally Without Uploading Manifests Cloud: about 19 hours of work at a blended $100/h, or $1,900 of principal carrying roughly $1.04 a day. State that number, then the single business outcome it protects, then ask for dated capacity. If the ask is declined, log it with a revisit trigger so the decision stays visible to the cto.